Web Application Development Security Checklist for Compliance, data audits, and hardening backend systems.
A robust security foundation is essential for meeting corporate compliance benchmarks and passing data security audits. Use this web application development checklist to harden your backend against vulnerabilities and protect critical assets:
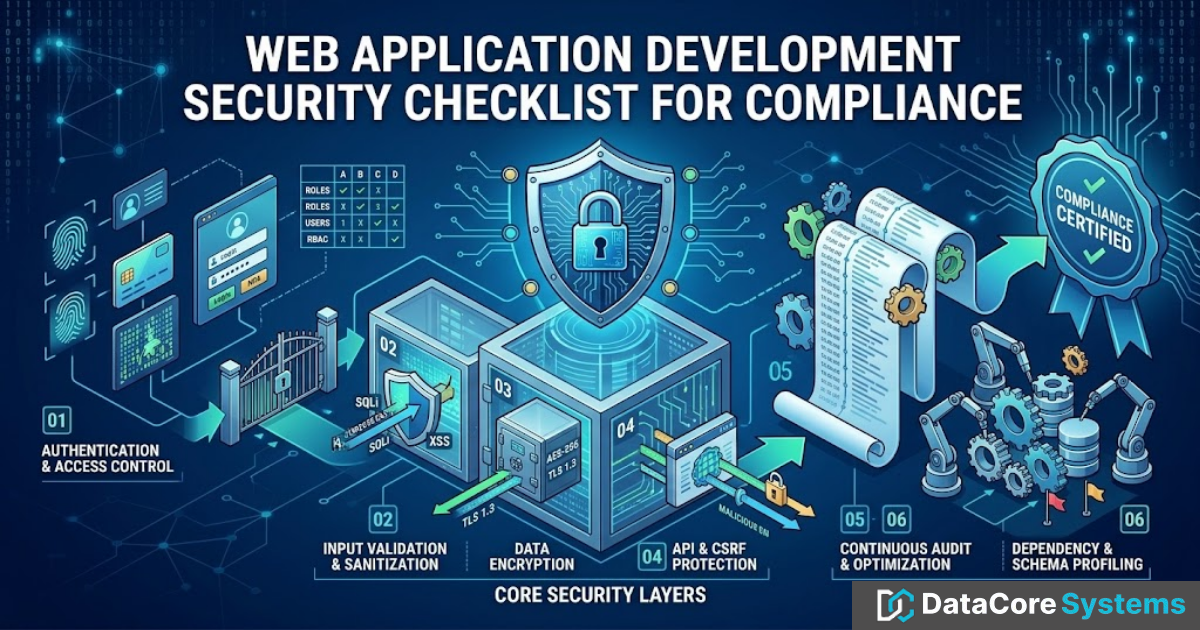
Core Compliance & Hardening Protocols
Authentication & Access Control: Enforce multi-factor authentication (MFA), strict role-based access control (RBAC), and secure session management to prevent unauthorized access.
Input Validation & Sanitization: Implement parameterized queries (prepared statements) to neutralize SQL injection (SQLi) and sanitize user inputs to prevent cross-site scripting (XSS).
Data Encryption: Encrypt sensitive data at rest using AES-256 and mandate TLS 1.3 for all data in transit across your web network.
API & CSRF Protection: Implement Anti-CSRF tokens for state-changing requests and apply rate-limiting to API endpoints to prevent brute-force attacks.
Audit Logging & Profiling: Maintain immutable, timestamped logs for all system transactions, administrative actions, and failed login attempts.
Dependency & Schema Profiling: Routinely profile database query execution and run automated vulnerability scans on third-party libraries and codebases.
Proactive security controls integrated directly into your system architecture significantly reduce technical risk, prevent expensive breaches, and streamline compliance verifications.
Need to clear rigorous data security audits? Contact DataCore Systems today to evaluate your backend architecture and secure your development pipeline.
Get in Touch